The automation of the SSL/TLS certificate renewal enables enterprises to cite its importance for online activities. However, the process of traditional DNS-01 validation may cause certain problems associated with constant updating of DNS records, using of provider APIs, and managing credentials. With the introduction of DNS-PERSIST-01, the principles of operation…
Multi-domain SSL certificates can be a good value when buying several domains, but many people are confused about the cost. This tutorial will show you how to choose the right domains and when to install multi-domain SSL instead of a different option. Multi-domain SSL is cheaper only if you want…
By March 15, 2029, maximum certificate lifetimes will fall to 47 days (down from 398), and domain validation reuse will drop to 10 days, with step-downs in 2026 and 2027 along the way. The challenge is no longer a small, snaggy setup concern; it’s now a design choice of what you…
Choosing the right SSL certificate depends on Domain Validated (DV), Organisation Validated (OV), and Extended Validation (EV). Most site owners know they should use HTTPS, but aren’t sure which level is best for their site. This guide simplifies the muddle by outlining the facts of the different levels and guiding…
On October 17, 2026, a security researcher reported that the private keys of eight intermediate CA certificates run by eMudhra, the Indian certificate authority behind the emSign brand, could be recovered. The keys had been generated with insufficient randomness. Within two hours, Google and Mozilla had pushed blocks to Chrome…
Customers in part of the provider’s East Japan region have been told their data may be lost for good, and that their own backups may be the only way to recover. A ransomware attack on IDC Frontier, one of Japan’s largest domestic cloud providers, has spread across the country’s digital…
Google revealed on October 6, 2026 that attackers have hijacked the administrators of three country-code domain registries to get illegitimate HTTPS certificates for a number of Google sites and other domain names. Google said it blocked the certificates in Chrome and that its own systems were not breached. What was…
March 15, 2027, cuts public TLS to 100 days. Manually renewing will not be the way to go through the chop. Six months left. On March 15, 2027, new public TLS drops to 100 days. TLS 200-day is now available. The renewal process will not change from twice a year…
Most of today’s data is encrypted using public-key algorithms that quantum computers can break. Security experts already harvest data from these machines that is encrypted and can be decrypted later. There is a need to act now at the organisational level. This guide provides assessment steps, a roadmap, a framework,…
Key Takeaways Introduction Different entities use separate PKIs, and each has a different root of trust. This makes it impossible for users to validate certificates and their identities between trust domains. To solve this problem, cross-certificates come into play, as they make connections between separate trust domains while maintaining certification…
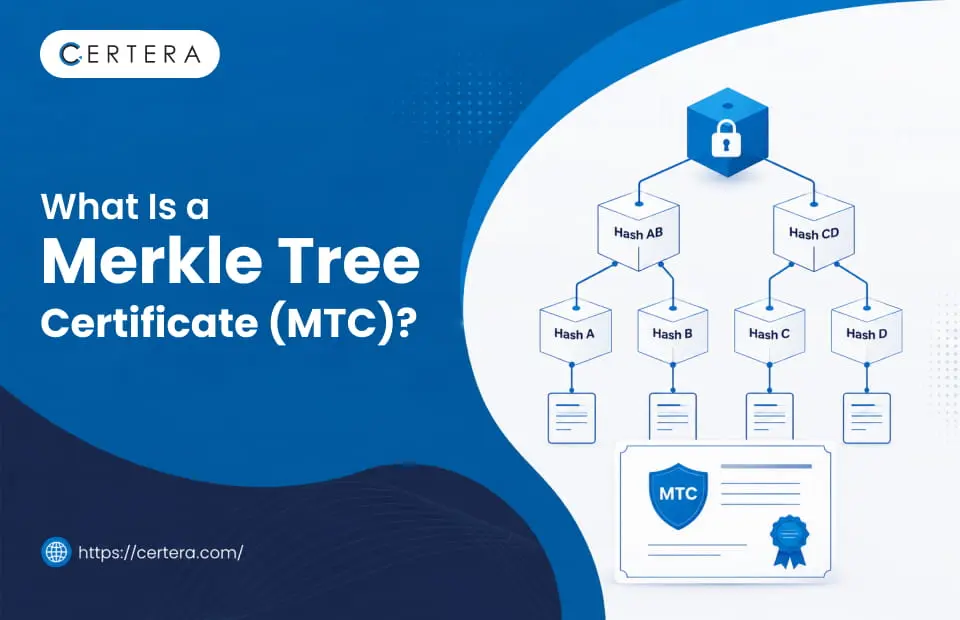
As businesses and organizations ramp up their utilization of digital certificate systems, there arises a need to be able to verify certificate-related data in an efficient manner, without subjecting large datasets to a cumbersome verification process again and again. Merkle Tree Certificates (MTCs) use cryptographic hash trees to create compact…
Hand-releasing SSL/TLS certificates no longer scales because it starts with a request. They did so by allowing servers to communicate directly with Certificate Authorities, but Let’s Encrypt’s registration is open, whereas enterprise CAs & commercial providers require verification of who they are issuing a certificate to. This is where External…
Quantum computers will not only become faster. They’ll get dangerous. After passing that threshold, they could break RSA and ECC encryption protecting your banking transfers, medical details, and “HTTPS” connections. Attackers aren’t waiting. They are currently collecting encrypted data, hoping to eventually be able to decrypt the information as quantum…
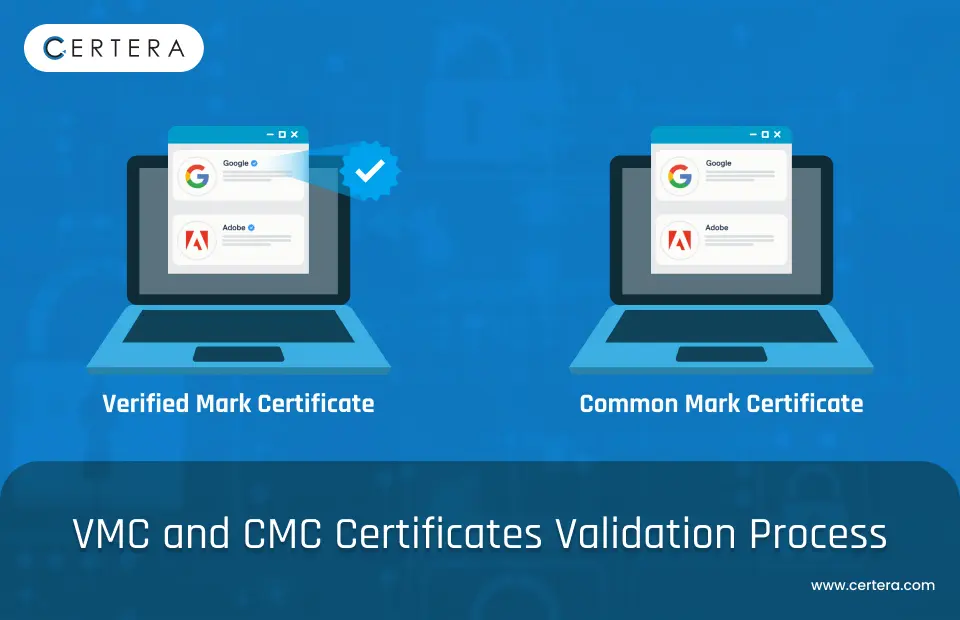
With the development of email security, Verified Mark Certificates (VMCs) and Common Mark Certificates (CMCs) have become critical for organisations that want to showcase their brand logos in email clients using the BIMI (Brand Indicators For Message Identification) standard. Before an organisation’s logo appears in a recipient’s inbox, however, it…
Your SSL pipeline breaks at 2 am… Does this sound like you? Nothing was going wrong at all. Certificates were issued. Renewals were automated. You felt confident. And your page gives a certificate warning. Now you’re scrambling and checking logs. Restarting services and asking yourself why some automatic thing just…